Manually scanning a business computer for viruses and hoping the backup already grabbed clean files is how businesses end up restoring the same infection twice. Instead of guessing which came first, run isolation, removal, and backup in a fixed order every time so the malware never gets copied into your restore point.
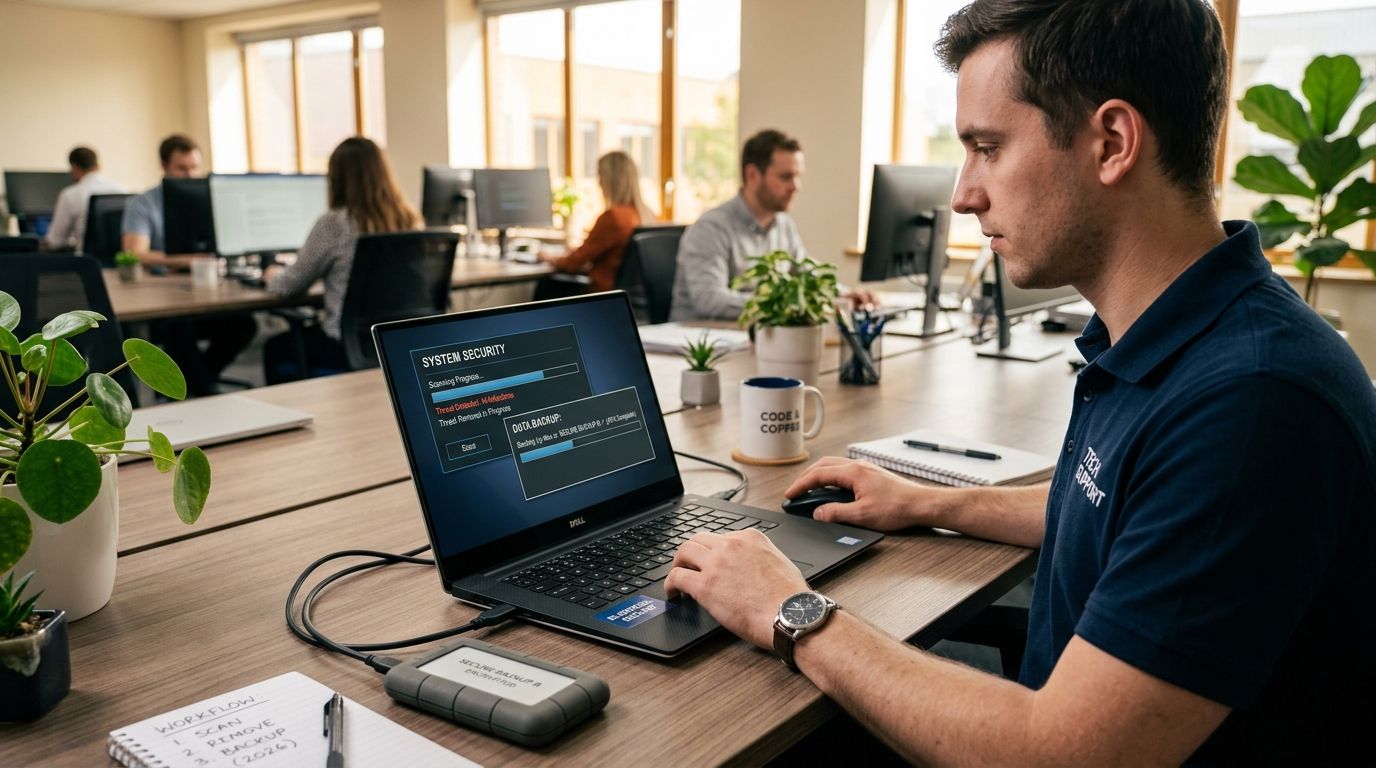
- A virus removal and backup workflow business computer needs in 2026 isolates the machine first, then scans twice before touching backup.
- Never back up an infected drive — cloud sync tools push malware into every connected folder within minutes.
- Two consecutive clean scans from two different engines confirm the machine is safe to reconnect.
- TechConnect LLC runs this exact order on same-day visits across North Carolina, starting with a free diagnostic.
Why this matters
A compromised business computer doesn't just slow down — it puts every synced drive, shared mailbox, and cloud folder at risk the moment it's reconnected to a network. Back up before you've confirmed the machine is clean and you've just created a malware-tainted restore point that undoes the cleanup the next time someone restores from it.
The order matters more than the tools. TechConnect LLC handles computer repair and virus removal for homes and businesses across North Carolina, and the pattern is consistent: businesses that back up before confirming a clean scan end up calling back within weeks because the same infection resurfaces from the restore point. Isolate first, remove second, verify third, back up last — every time, no shortcuts.
Before you start
- Admin access to the infected machine (local admin password) and to your backup destination — cloud storage login or the external drive's encryption key if one is set.
- A second, clean device to download removal tools. Never trust the infected machine's browser to fetch anything if it's already compromised — some malware redirects security-tool downloads to fake installers.
- The gotcha: a lot of malware disables Windows Update and blocks antivirus installers by filename. If an installer refuses to launch, rename the .exe file to something generic before running it — this alone clears a surprising number of blocks.
Isolate and confirm the infection
- Disconnect the machine from Wi-Fi and unplug the Ethernet cable immediately. Closing the browser or opening Task Manager first gives the malware more time to spread across the network.
- Write down every shared drive, email account, and cloud folder — Google Drive, Dropbox, OneDrive — that was actively syncing on this machine before you pulled the plug. You'll need this list for the recovery step later.
- If you need internet access to download removal tools, boot into Safe Mode with Networking rather than reconnecting the machine to the full network.
Expected result: the machine is fully off the network and you have a written list of every account it touched.
Run the removal pass
- From the clean device, download a reputable on-demand scanner onto a USB drive.
- On the infected machine, open Task Manager, sort by CPU and network usage, and end any unfamiliar process consuming resources it shouldn't.
- Run the on-demand scanner in full/deep scan mode and remove everything it flags — don't quarantine and move on, remove it.
- Reboot, then run Windows Security > Virus & threat protection > Scan options > Full scan as a second pass with a different engine. One scanner rarely catches everything; two consecutive clean scans is the actual bar.
Expected result: two consecutive clean scans from two different scanning engines, with zero remaining detections.
Configure real-time protection
- Turn on Windows Defender or install a dedicated endpoint protection software if the machine doesn't already have business-grade coverage running.
- In Windows Security settings, enable Tamper Protection and Cloud-delivered protection so the same malware family can't disable your antivirus again if it comes back.
- Set Windows Update to check daily instead of the default weekly cadence. Most reinfections trace back to a Patch Tuesday update that sat unapplied for months.
Expected result: real-time protection active, tamper protection on, and updates scheduled to check daily.
Rebuild the backup
- Only after two clean scans, reconnect the machine to your backup destination — cloud service or external drive.
- Run a full backup, not an incremental one. An incremental backup layered on top of older infected snapshots can still carry a copy of the malware forward.
- Verify the backup by opening two or three restored files directly, not by trusting the success notification alone.
- Follow the 3-2-1 rule going forward: three copies of your data, on two different media types, with one copy offsite. A single external drive sitting next to the computer it backs up doesn't survive theft, fire, or a second infection.
Expected result: a verified, malware-free backup with a fresh timestamp and at least one offsite copy.
“The cleanup only counts if the backup survives it — verify the restore, don't trust the success notification.”
Running this workflow on a schedule instead of after an incident
If you're not responding to an active infection, this same order works as routine maintenance rather than emergency triage:
- Scan first, confirm clean, back up second — monthly at minimum for a single-office business computer.
- Automate the sequence so the backup runs 24 to 48 hours after the scan completes, not the same day. Running both simultaneously means the backup can start before the scan finishes flagging something.
- Log the scan result before the backup job kicks off. If the scan found and removed anything, delay the backup until a second clean scan confirms it.
This turns the reactive version of the workflow into a repeatable business habit instead of something you only think about after a machine is already infected.
Get a free diagnostic before you back up
Same-day virus removal and backup verification across North Carolina.
Troubleshooting
- Antivirus installer won't launch. Rename the .exe file to a generic name before running it — some malware blocks installers by matching known security-tool filenames.
- Backup software can't see the drive after cleanup. Malware sometimes tampers with the boot sector or drive letter assignment. Check Disk Management for a missing or reassigned letter before assuming the drive failed.
- Files are missing or renamed, not just hidden, after removal. This points to ransomware encryption, not a standard virus. Stop before backing up the current state — restoring from an earlier clean point is safer, and the data recovery workflow covers what to do when files are unreadable rather than deleted.
- Scan comes back clean but network activity stays high. A second dropper is likely still running. End the process in Task Manager and rerun the full scan before touching the backup step at all.
- Backup takes far longer than normal. Check for renamed extensions like .locked or .crypt hiding among your files — encrypted duplicates inflate backup size and time without triggering an antivirus alert.
Customize your workflow
A single-computer workflow doesn't scale to an office with 10 or 20 machines without a plan for password resets, shared drive permissions, and update scheduling across every endpoint at once. If this incident touched a shared network, review network security practices before reconnecting anything else, and confirm every machine on that network runs the same real-time protection standard, not just the one that got infected.
2026 is a reasonable year to move off ad-hoc backups entirely and onto a scheduled, verified routine — the workflow above works as a one-time fix or a recurring habit, and the recurring version is the one that actually prevents the next call.
FAQ
What's the right order for virus removal and backup on a business computer?
Isolate the machine from the network first, run two clean scans with different engines, then back up. Backing up before confirming a clean scan risks copying the malware into your restore point.
Can I back up an infected computer before removing the virus?
No. Backing up an infected drive first can push malware into every synced cloud folder within minutes and creates a tainted restore point you'll need to clean again later.
How many scans does it take to confirm a business computer is clean?
Two consecutive clean scans from two different scanning engines is the standard bar. One scanner alone often misses secondary droppers or hidden processes.
What is the 3-2-1 backup rule?
The 3-2-1 rule means keeping three copies of your data, on two different media types, with one copy stored offsite. A single external drive next to the computer doesn't count as a real backup strategy.
How do I know if it's a virus or ransomware?
If files are missing, renamed with extensions like .locked or .crypt, or unreadable rather than simply infected, treat it as ransomware and stop before backing up the current state. Restore from an earlier clean backup instead.
How often should a small business run this virus removal and backup workflow?
As routine maintenance, run the scan-then-backup sequence monthly at minimum, with the backup automated to start 24 to 48 hours after the scan completes.
Does Windows Defender count as real-time protection for a business computer?
Windows Defender with Tamper Protection and Cloud-delivered protection enabled provides baseline real-time coverage, though many small businesses pair it with dedicated endpoint protection software for centralized monitoring.
What if the backup itself won't run after cleanup?
Check Disk Management for a missing or reassigned drive letter first — some malware tampers with the boot sector, which can make a healthy drive look inaccessible to backup software.
One last thing
The step everyone skips is opening the restored files after the backup finishes. A backup that completes with a green checkmark can still contain corrupted or partially encrypted files if the scan wasn't actually clean when the backup started — open two or three files directly before trusting the job.